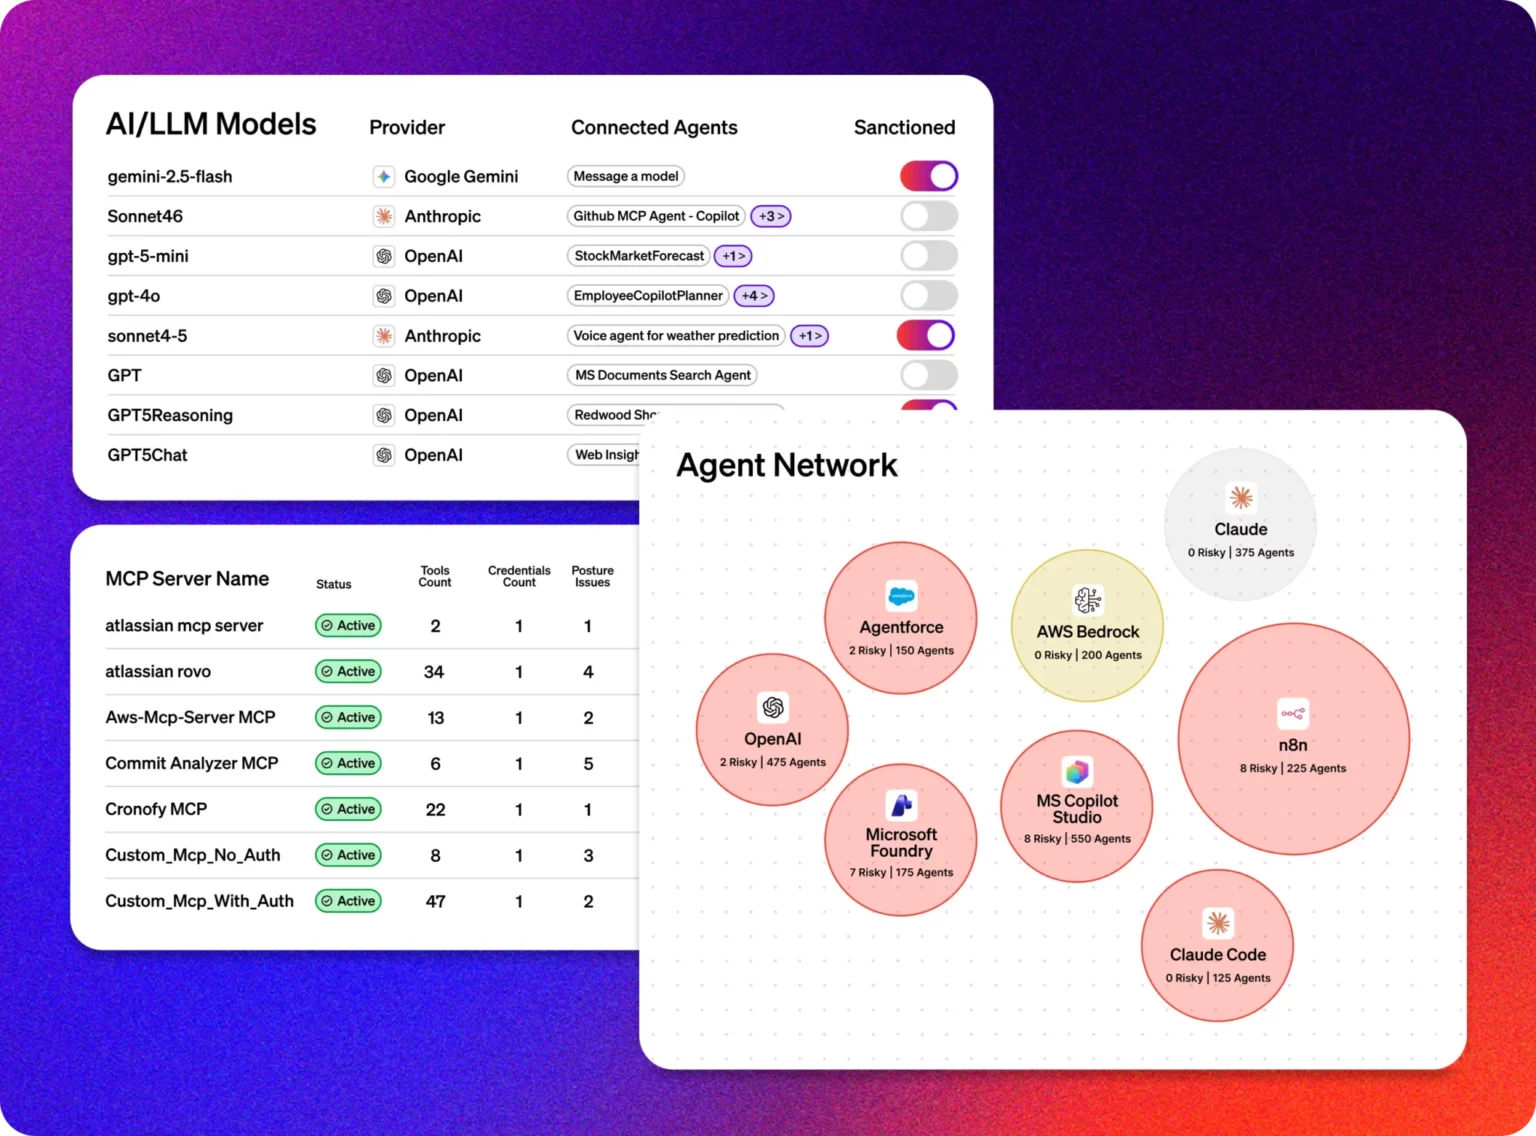
AppViewX brings visibility, automation and governance to certificates, keys, machine identities and AI agents, helping organizations build digital trust for cryptographic change and the post-quantum era.
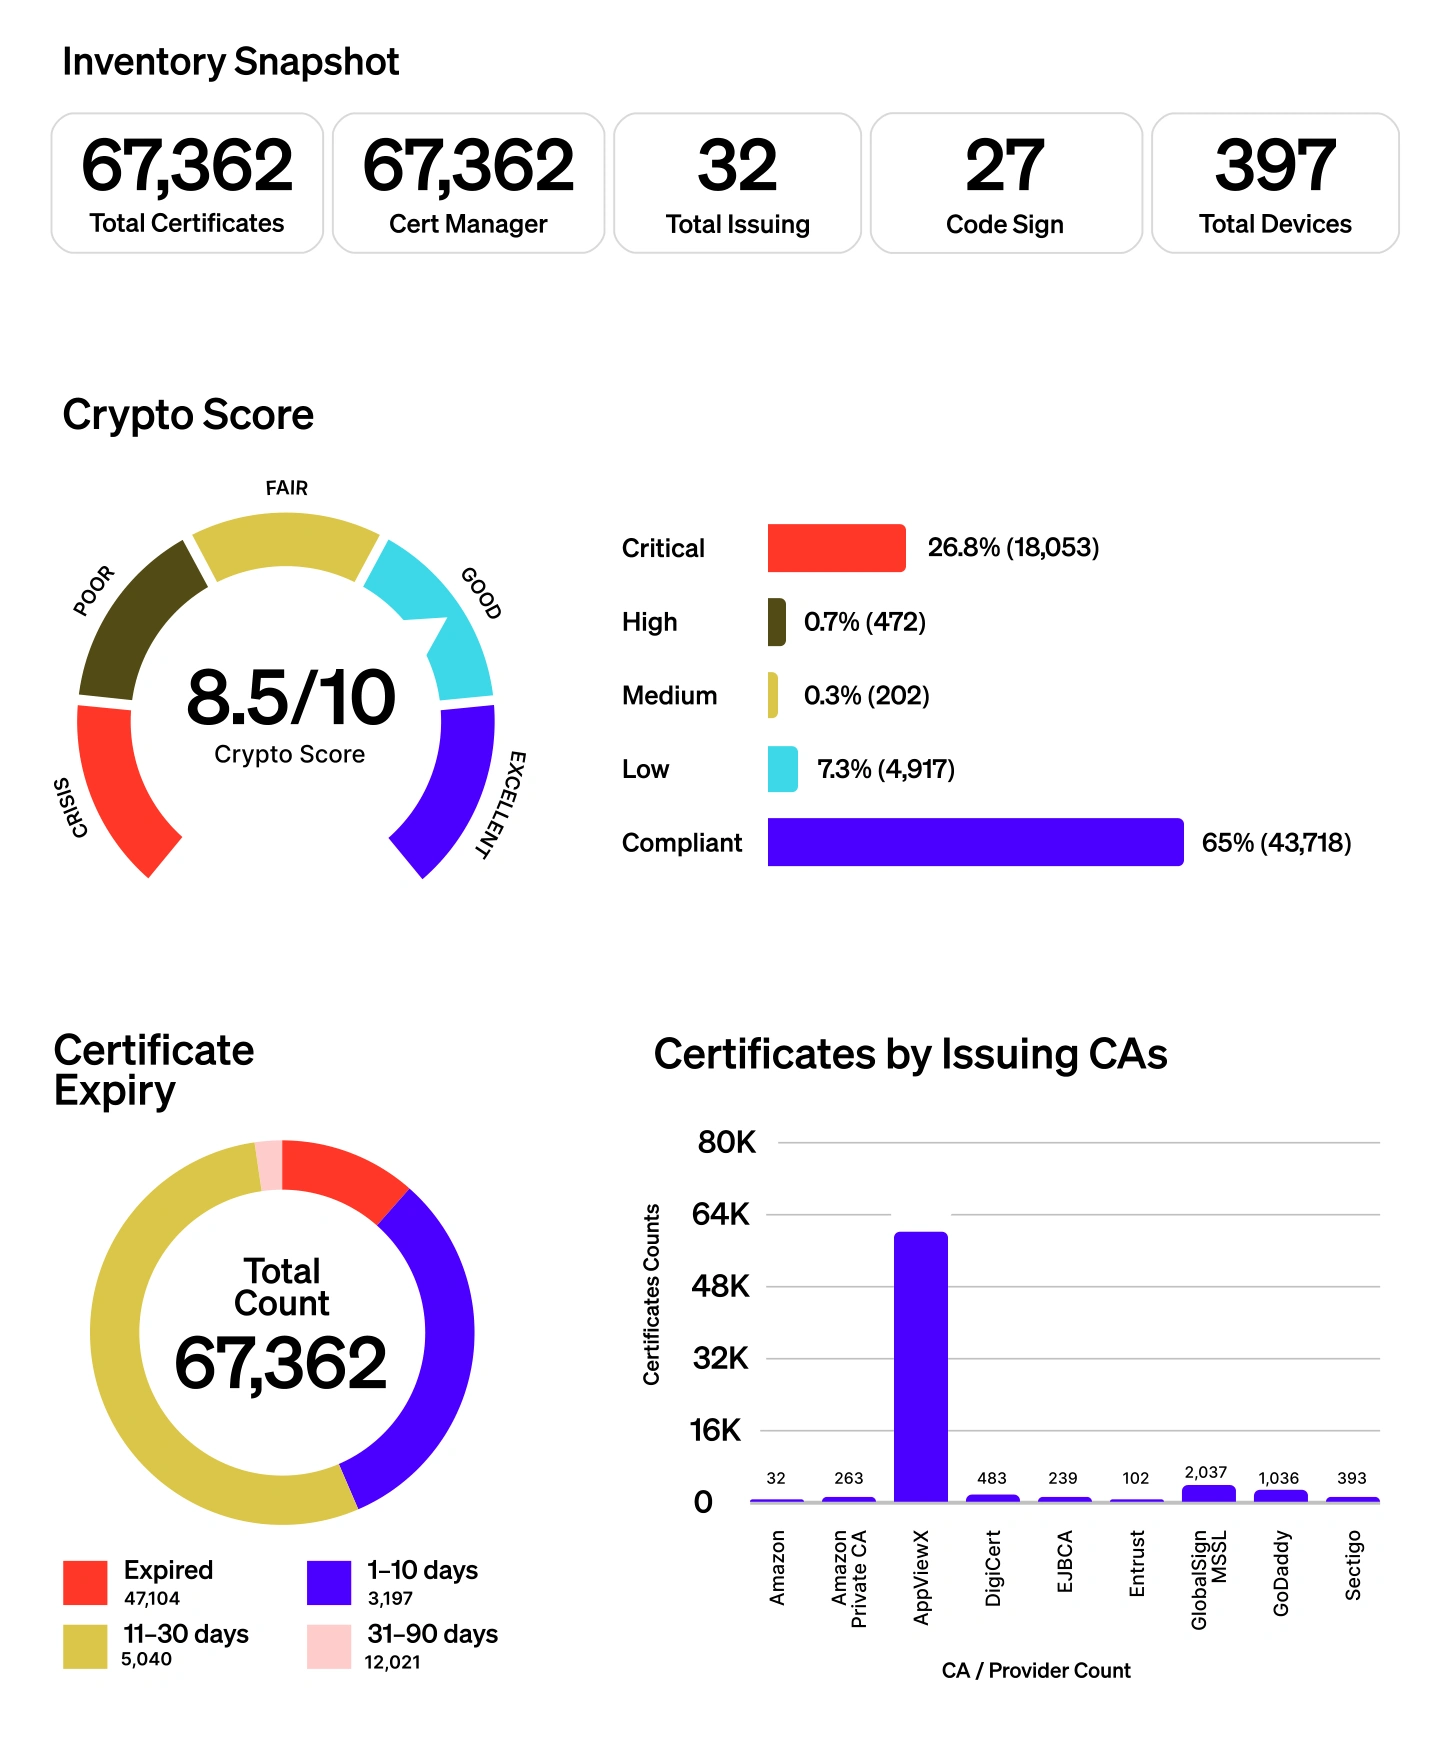
CLM at a glance · official AppViewX interface illustration with demo data.
Machine identities + AI agentsShared visibility and policy, with purpose-built controls for each domain.
Discovery
Automation
Governance
Crypto-Agility
PQC Readiness
THE CYBERLION PERSPECTIVE
Digital trust needs management, not manual work.
Certificates, keys and non-human identities run through applications, cloud, devices, Kubernetes and DevOps. AI agents now connect to business systems and information, too. AppViewX brings together the visibility, policy and automation needed to manage this trust consistently.
✓A central view of identities, certificates and keys.
✓Automation for manual, error-prone processes.
✓Policy and controls that adapt to changing environments.
AVX PLATFORM · TWO DOMAINS, ONE FOUNDATION
Trust between systems. Control for every agent.
AVX Platform
A shared layer of control, policy and automation across products and modules.
Discovery
Automation
Governance
Policy
Manage the trust that connects your systems.
Discover and manage the certificates, keys and identities used by servers, applications, devices, cloud workloads and DevOps workflows.
✓Certificates, PKI, SSH keys and code signing.
✓Kubernetes certificates and application delivery infrastructure.
Ready for shorter certificate lifetimes and the post-quantum era.
47-day readiness
✓Discover certificates and assign ownership.
✓Automate renewal, deployment and domain control validation.
✓Reduce dependence on manual processes.
Crypto-Agility & PQC
✓Discover algorithms, keys and cryptographic dependencies.
✓Create a Cryptographic Bill of Materials · CBOM.
✓Assess risk, define policy and plan migration to new cryptography.
200 daysmaximum validity
100 daysmaximum validity
47 daysmaximum validity
Maximum validity for newly issued publicly trusted TLS certificates under the CA/Browser Forum schedule; this is not the validity of every certificate type. View the official SC081v3 schedule ↗
PQC capabilities, supported algorithms and modules depend on version, licensing and the integrated systems.
THE COMPLETE PORTFOLIO
Choose a domain. Explore the products.
AVX Platform is the shared foundation. Select a tab to explore the relevant core products and dedicated modules.
SHARED PLATFORM
AVX Platform
Control, policy and automation for AppViewX products and modules.
Official AppViewX product illustration · demo data.
Capabilities, deployment models and integrations depend on product, version, licensing and configuration. CyberLion will help assess the fit for your environment.
PKI + CLM
Create trust and manage it on the same platform.
PKI
PKI establishes the authority of trust and issues certificates. It provides the foundation for trusted identities and communication within your organization.
CLM
CLM discovers, deploys, renews, revokes and governs certificates throughout their lifecycle, across public CAs and private PKI.
Root of TrustTrust authority
CertificateDigital credential
SystemServer or system
ApplicationApplication or service
A conceptual trust path. PKI and CLM complement each other; the connection is tailored to your enterprise architecture.
START WITH YOUR NEEDS
What would you like to automate and govern?
Reduce outages caused by expired certificates.
Automate certificate lifecycle management.
Modernize or migrate existing PKI infrastructure.
Prepare for shorter certificate lifetimes.
Build crypto-agility and PQC readiness.
Manage Kubernetes and DevOps certificates.
Manage SSH keys and access.
Secure code-signing workflows.
Discover and govern AI agents.
DEPLOYMENT & INTEGRATIONS
Manage trust in the environment you already use.
CLM supports the following deployment models, aligned with your operational, infrastructure and regulatory requirements.
SaaS
A fully managed cloud service.
Private Cloud
Deploy in your private cloud.
Hybrid
Connect cloud and local infrastructure.
On-Prem
Deploy on your own infrastructure.
Connect to your existing workflows.
Certificate Authorities
Cloud Platforms
Kubernetes & Containers
HSM
DevOps & CI/CD
Load Balancers
ITSM & Security
Validate the systems, versions and connection methods you need with CyberLion. Not every integration or deployment model is available for every product.
TRUST YOU CAN VERIFY
Clear sources. Informed decisions.
AppViewX Trust Center
Official vendor information on security and compliance, with access to available documents and a process to request further information subject to permissions.
Content was checked against the AppViewX website and version 2026.3.0 documentation. Components, modules and integrations are selected around your business needs.