The need
Assets and findings are spread across multiple clouds.

ACCUKNOX × CYBERLION | ZERO TRUST CNAPP
From code to runtime — visibility, context and enforcement in one platform.
AccuKnox brings code, cloud, Kubernetes, workload and AI security together so organizations can identify risk, prioritize it using operational context and enforce Zero Trust policies at runtime.
THE CYBERLION PERSPECTIVE
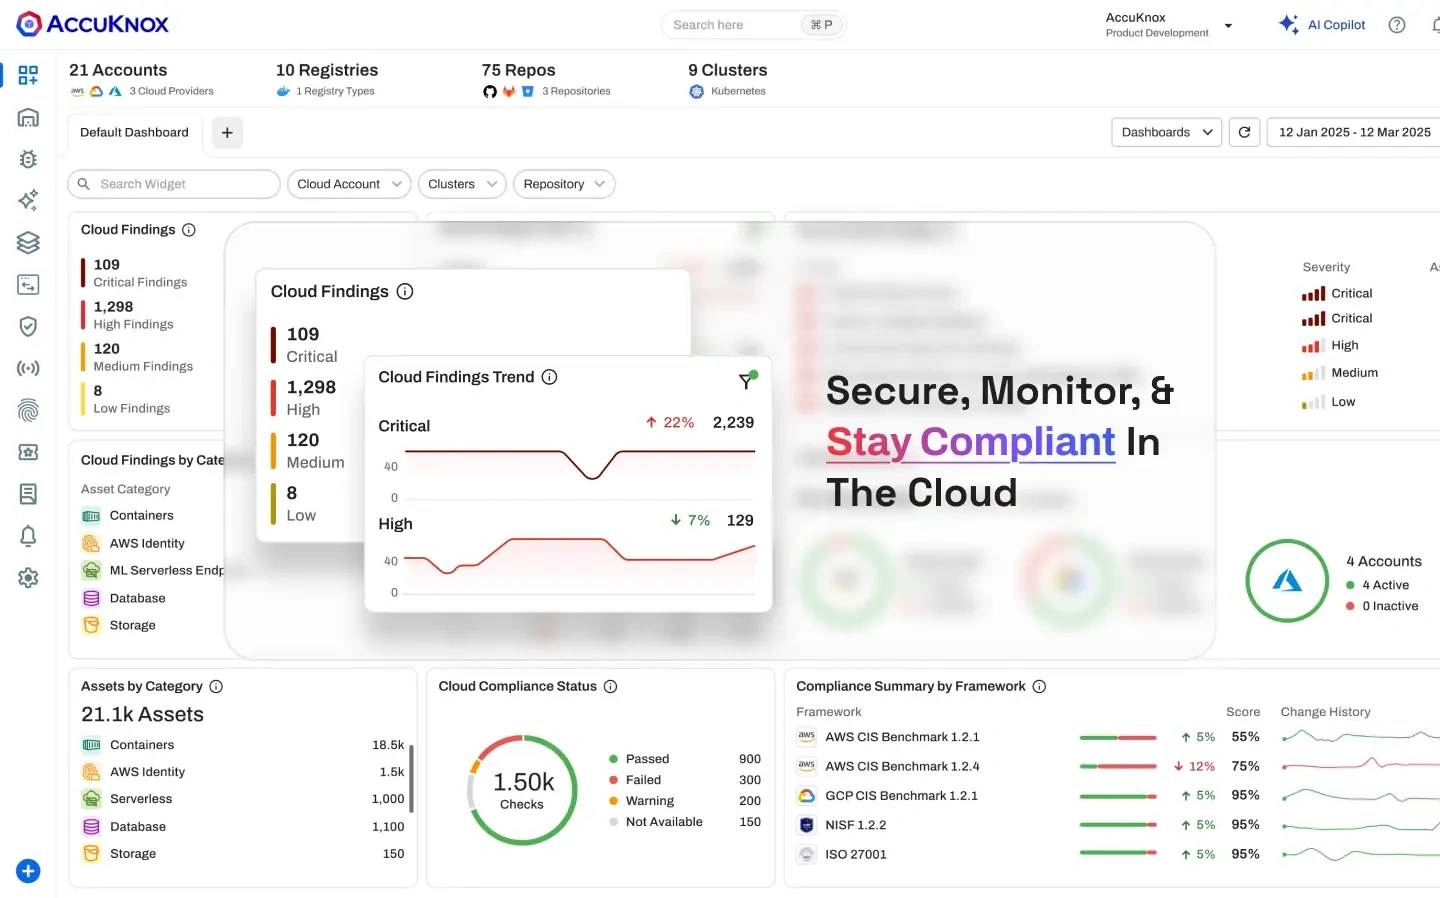
Scans reveal vulnerabilities and misconfigurations. Security teams still need to understand what is reachable, what is running in production and what to address first. AccuKnox connects code and cloud findings with workload behavior at runtime.
A connected workflow from finding to response.
ONE PLATFORM. FIVE PROTECTION LAYERS.
Choose a layer to see what it protects and how it fits your workflow.
Secure Code
Pipeline scanning brings code, dependency and configuration findings together, then connects them to the assets that are actually deployed.
Secure Cloud
Central visibility into assets and configurations helps teams track security posture as cloud environments change.
Secure Workloads
Protect supported workloads across containers, Kubernetes, virtual machines and bare metal with context from runtime activity.
Secure Data, APIs & Secrets
Connect API discovery, sensitive-data findings and secrets management to reduce exposure and control access to important assets.
DSPM appears in the current product page and documentation, while some vendor catalog pages still label it Beta. We will confirm its availability status for your selected version and offering before a proposal.
Secure AI
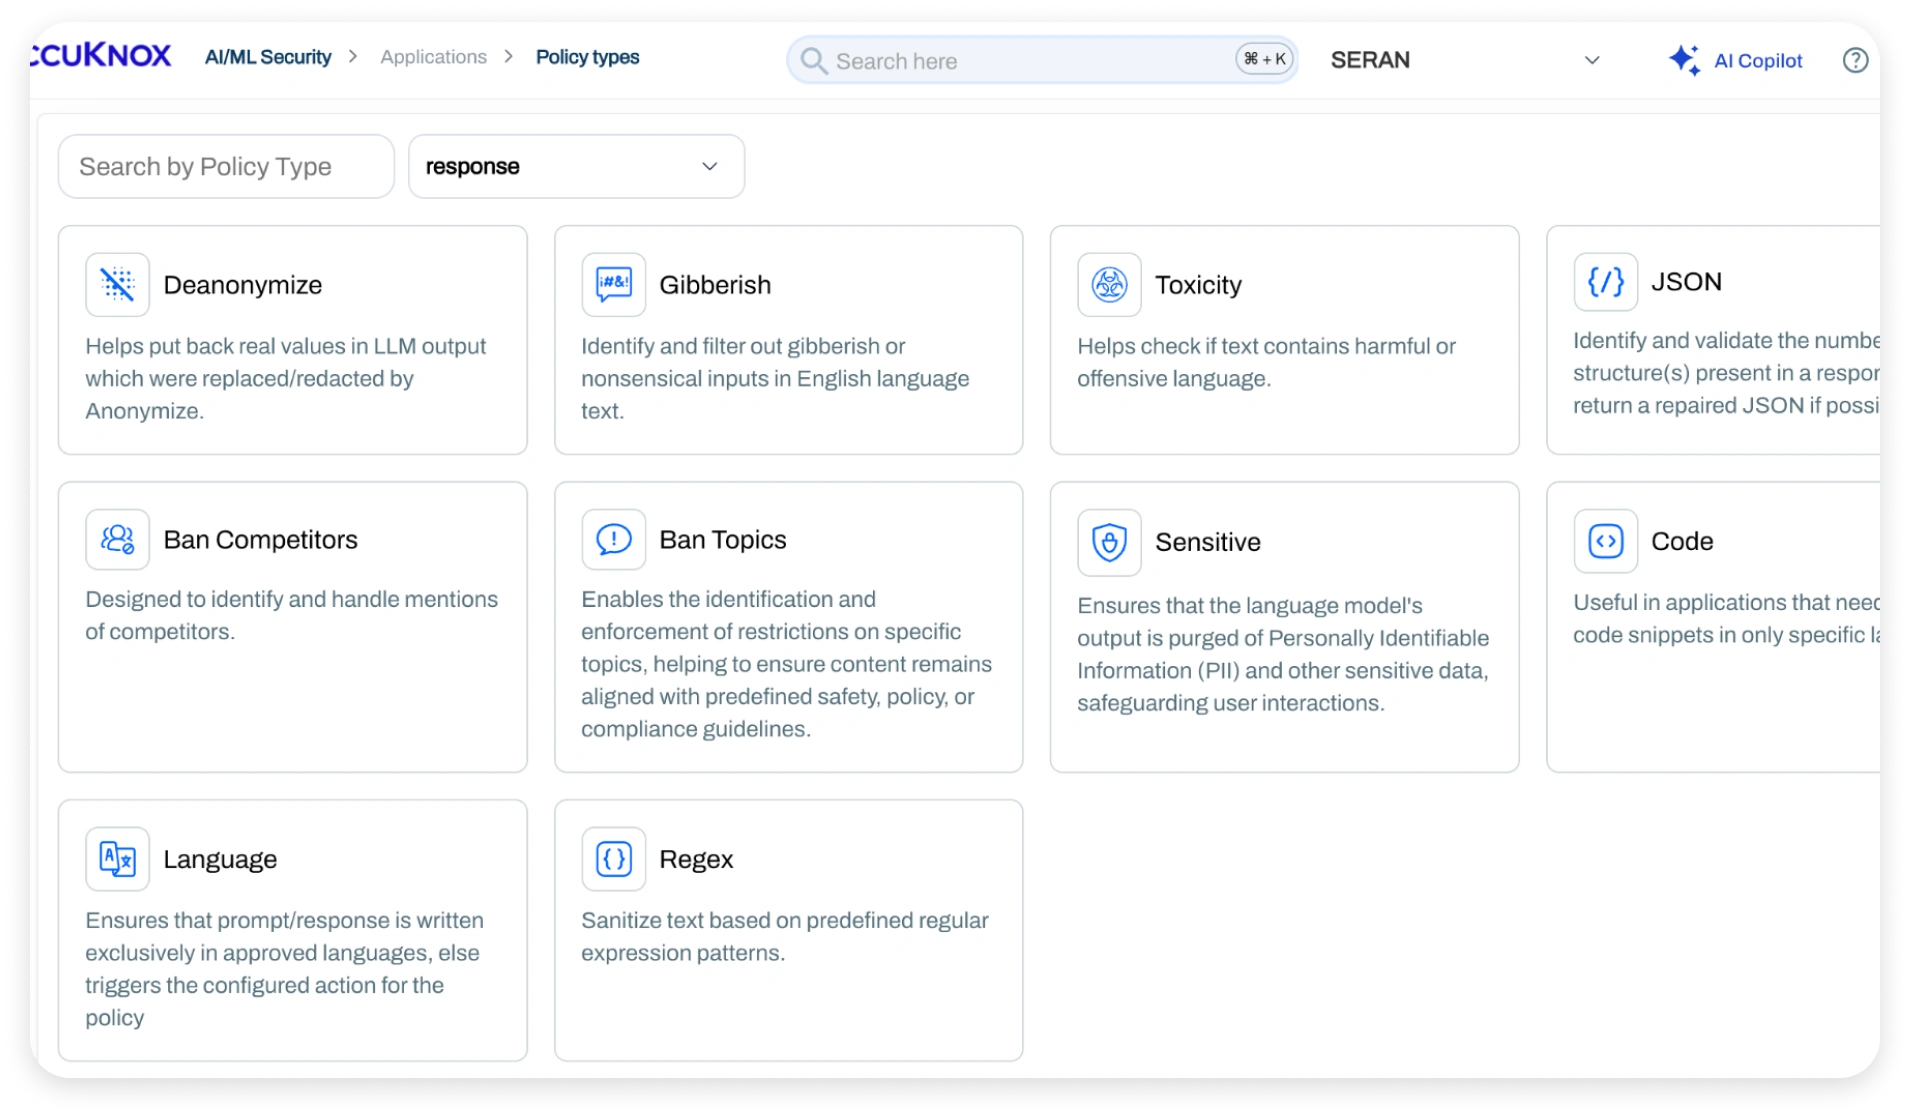
Extend the security continuum to AI assets, from discovery and inventory to model testing, prompt protection and agent activity controls.
THE RUNTIME DIFFERENCE
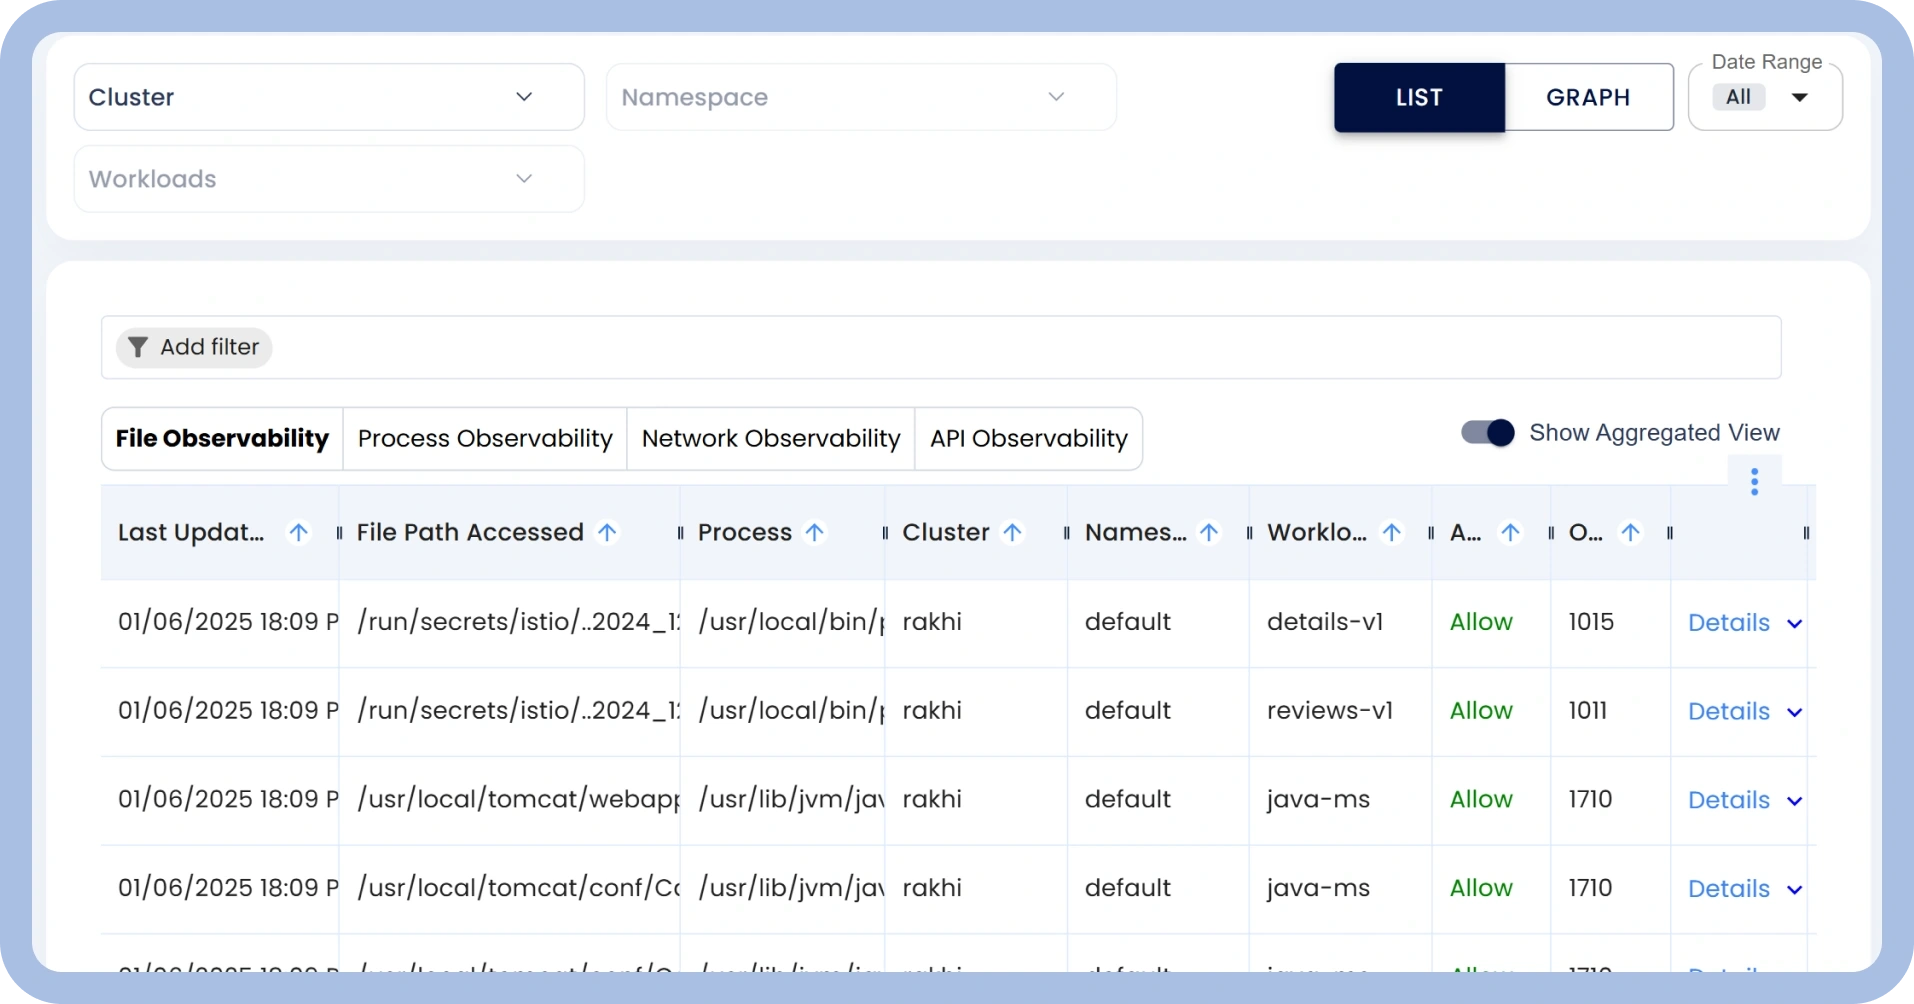
AccuKnox combines eBPF telemetry with Linux Security Modules enforcement in supported environments. Teams can learn from activity, review policies and move from Audit mode into controlled enforcement.
Observe workload activity.
Identify behavior and required permissions.
Review and approve policy in Audit mode.
Enforce policy and follow the outcome.
KubeArmor is the open-source project behind certain runtime capabilities. It provides a foundation for visibility and enforcement; AccuKnox enterprise management, policy discovery and integrations are assessed separately.
Agentless scanning provides visibility. Runtime enforcement requires supported components and environments. We will validate your operating system, kernel and infrastructure.
CNAPP IN PLAIN LANGUAGE
A full name, a clear purpose and a practical benefit — without assuming you know every acronym.
Cloud Security Posture Management
Find misconfigurations, track changes and map findings to policy.
Capability detailsKubernetes Security Posture Management
Review cluster configuration and hardening to reduce configuration risks.
Capability detailsCloud Workload Protection Platform
Runtime visibility and protection for supported containers, virtual machines and workloads.
Capability detailsApplication Security Posture Management
Bring code, dependency and application findings together with environment context.
Capability detailsAPI Security
Discover APIs, assess exposure and review interface policies and access.
Capability detailsCloud Detection and Response
Connect cloud events and operational context to support investigation and response priorities.
Capability detailsData Security Posture Management
Discover and classify sensitive information with visibility into location and exposure.
DSPM appears in the current product page and documentation, while some vendor catalog pages still label it Beta. We will confirm its availability status for your selected version and offering before a proposal.
Capability detailsSecurity Information and Event Management
Collect, correlate and analyze events to support investigation and response.
Capability detailsSecrets Management · SCA · SBOM
Manage access credentials and inventory software components to reduce development-lifecycle exposure.
Capability detailsDEPLOYMENT FOR YOUR ENVIRONMENT & POLICY
Compare the control-plane location, data path and environment suited to each model.
| Deployment model | SaaS | Your cloud | On-Premises | Air-Gapped |
|---|---|---|---|---|
| Control-plane location | AccuKnox cloud. | Your cloud account. | Your servers. | Your isolated network. |
| Data path | Scan results go to the vendor’s control plane. | Security data stays in your account; product updates are pulled. | Local management and telemetry; updates depend on deployment. | No outbound traffic or call-home in the isolated model. |
| Best suited to | Teams preferring a managed service and rapid evaluation. | Organizations needing data-residency control. | Organizations managing security inside their data center. | Environments with strict isolation requirements. |
This summarizes the vendor’s deployment models. External connections, updates, features and supported components are defined during deployment planning.
VALUE FOR YOUR TEAMS
Choose a team to explore its need, workflow and practical outcome.
Assets and findings are spread across multiple clouds.
Centralize inventory, review configurations and map findings to policies and context.
A consolidated picture and clearer risk priorities.
Development findings do not always connect to the asset running in production.
Embed scanning in CI/CD and link code, components, images and runtime environments.
Fix earlier and keep context after deployment.
Clusters and workloads change, and policy needs to follow actual activity.
Assess configuration, learn behavior and progress from Audit to enforcement and microsegmentation.
Control workload activity rather than adding another list of alerts.
Models, prompts and agents introduce new asset types and actions.
Discover AI assets, test models and configure guardrails and agent controls according to available capabilities.
Visibility and control over AI use, data access and agent actions.
COMPLIANCE, EVIDENCE & CONNECTIONS
Link findings to relevant frameworks and controls.
Reports, telemetry and records to support audit workflows.
Connect supported cloud, DevOps, ticketing and security tools.
Technology transparency around KubeArmor alongside enterprise platform capabilities.
Control mapping does not certify your organization. Coverage and integrations are validated against your environment.
ACCUKNOX × CYBERLION
We will review your cloud environment, development workflows, workloads and AI applications, then map the AccuKnox modules that fit your infrastructure and required deployment model.